
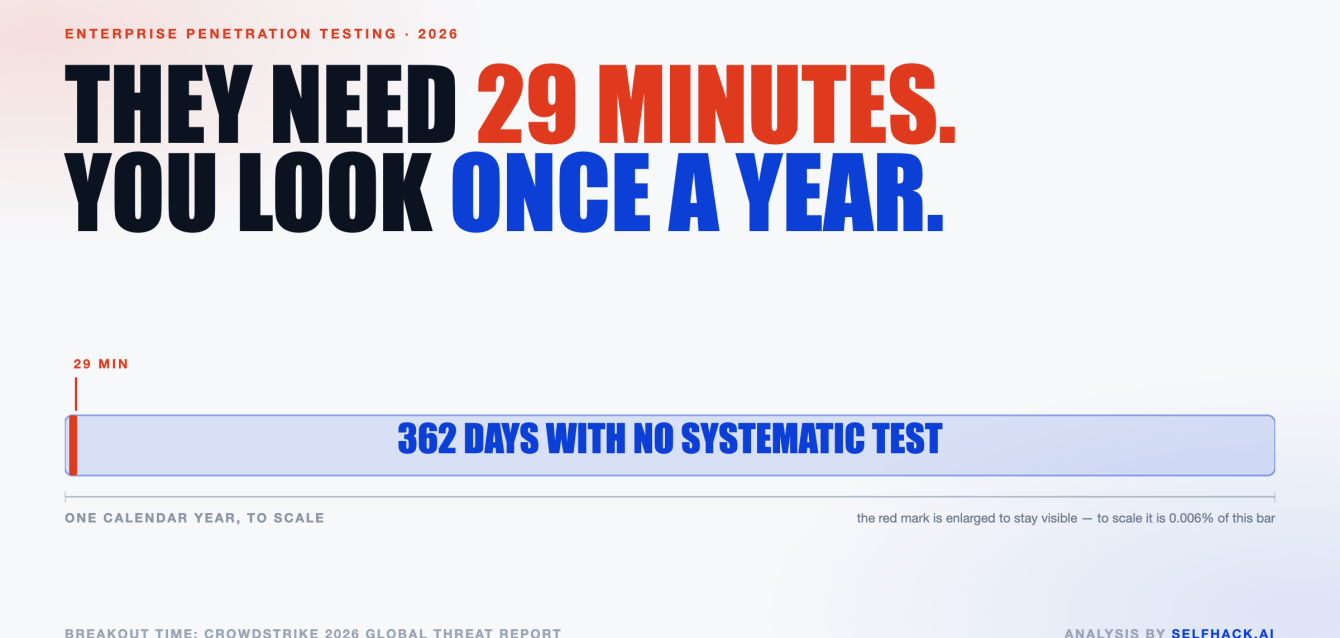
Enterprise penetration testing in 2026: attackers break out in 29 minutes and use AI at scale, so annual testing no longer matches the threat.
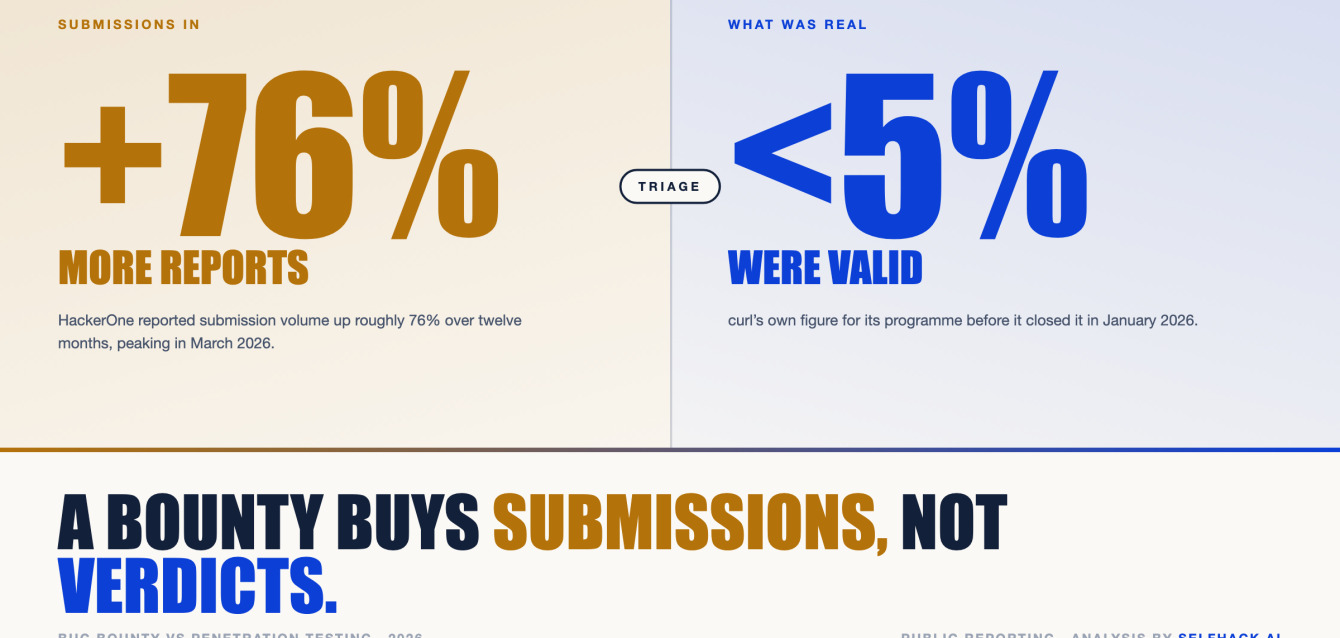
Bug Bounty vs Penetration Testing in 2026: What the AI Submission Wave Actually Changed
Bug bounty vs penetration testing in 2026: what the AI submission wave changed, what each model is genuinely good at, and where agentic testing fits.
DORA Penetration Testing: Who Is in Scope, What Threat-Led Testing Means, and How to Prepare
DORA penetration testing: who is in scope, what threat-led testing (TLPT) means under EU 2022/2554, and how continuous testing keeps you ready.
ISO 27001 Penetration Testing: Which Clauses It Supports and How to Run It for the Audit
ISO 27001 penetration testing: which clauses and Annex A controls it supports, what the auditor wants, and why continuous keeps your ISMS current.
HIPAA Penetration Testing: How to Satisfy the Security Rule When It Never Says Pentest
HIPAA penetration testing: how a test satisfies the Security Rule’s risk analysis and evaluation, and why continuous beats an annual snapshot.
PCI DSS Penetration Testing: Requirement 11.4, Segmentation, and the Significant-Change Trap
PCI DSS penetration testing: what Requirement 11.4 demands, and the significant-change trap that catches teams between annual audits.
SOC 2 Penetration Testing: Where It Fits, What Auditors Expect, and How Often to Run It
SOC 2 penetration testing: where it fits in the Trust Services Criteria, what auditors expect in the report, and how often to run it.
Compliance Penetration Testing: What SOC 2, PCI DSS, HIPAA, ISO 27001 and DORA Actually Require
Compliance penetration testing: what SOC 2, PCI DSS, HIPAA, ISO 27001 and DORA each require, and why continuous testing beats an annual certificate.
Autonomous Cyber Attacks: What Anthropic’s Threat Report Means for Your Next Pentest
Autonomous cyber attacks are here: what Anthropic’s September 2026 threat report shows, and why an annual pentest cannot answer machine-speed adversaries.
SSL/TLS Check: How to Test Your Certificates and Protocol Configuration
SSL TLS check: certificate validity and chain, protocol versions, cipher suites and HSTS — what each result means and what to fix first.