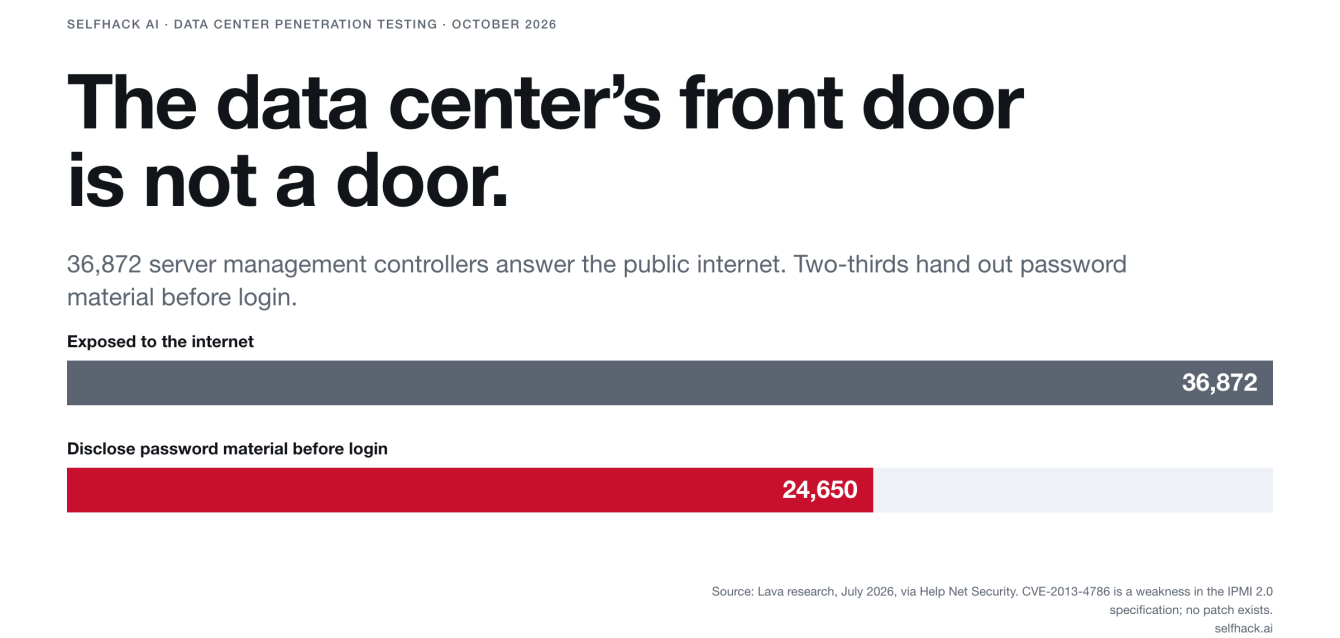
Data center penetration testing explained: discover what a remote test of BMCs, hypervisors, DCIM, out-of-band networks and facility OT can prove.
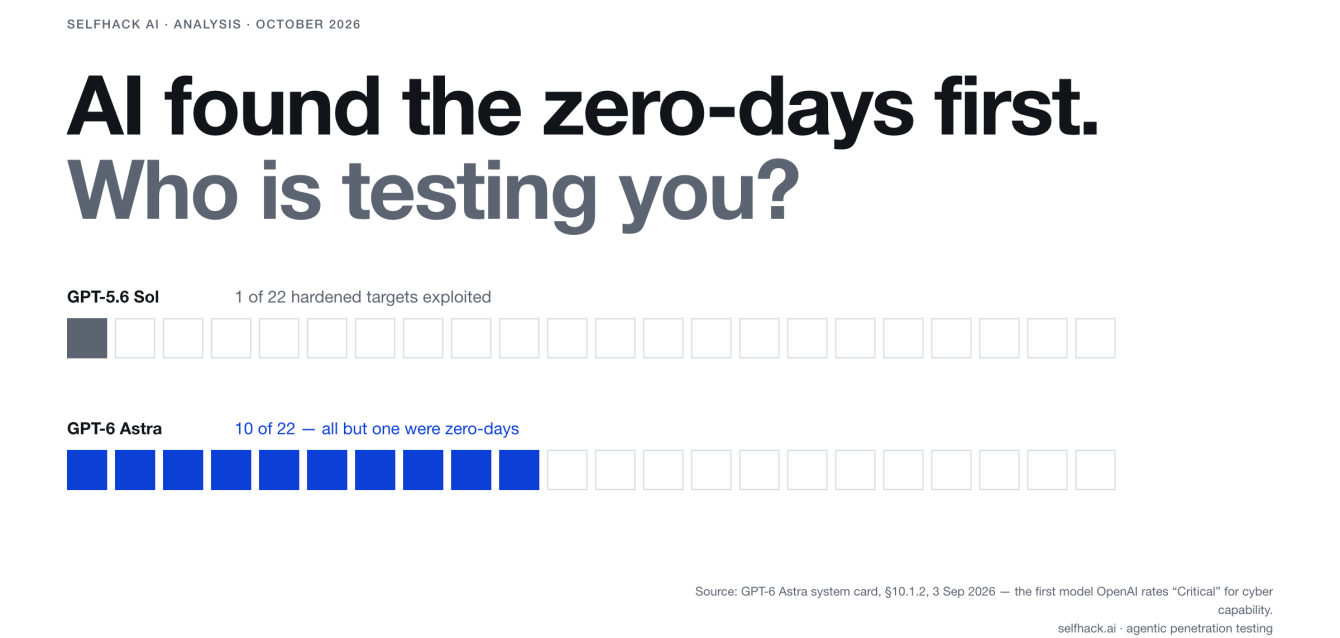
Agentic Penetration Testing After PHP2Shell: AI Found the Zero-Days First. Who Is Testing You?
Agentic penetration testing explained after PHP2Shell: learn why AI finding zero-days first means your estate needs autonomous, continuous testing.
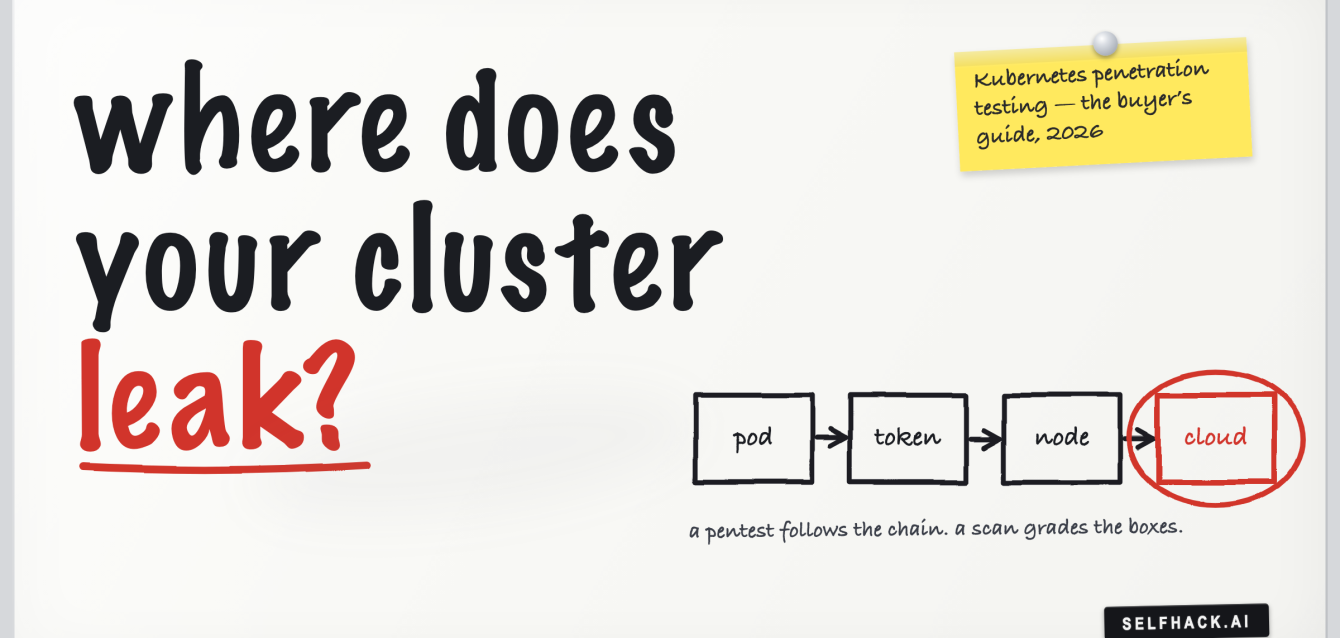
Kubernetes Penetration Testing: What a Real Test Covers, and Why a Config Scan Isn’t One
Kubernetes penetration testing explained for buyers: what a real test covers, why kube-bench/Kubescape scans aren’t one, and how to scope it.
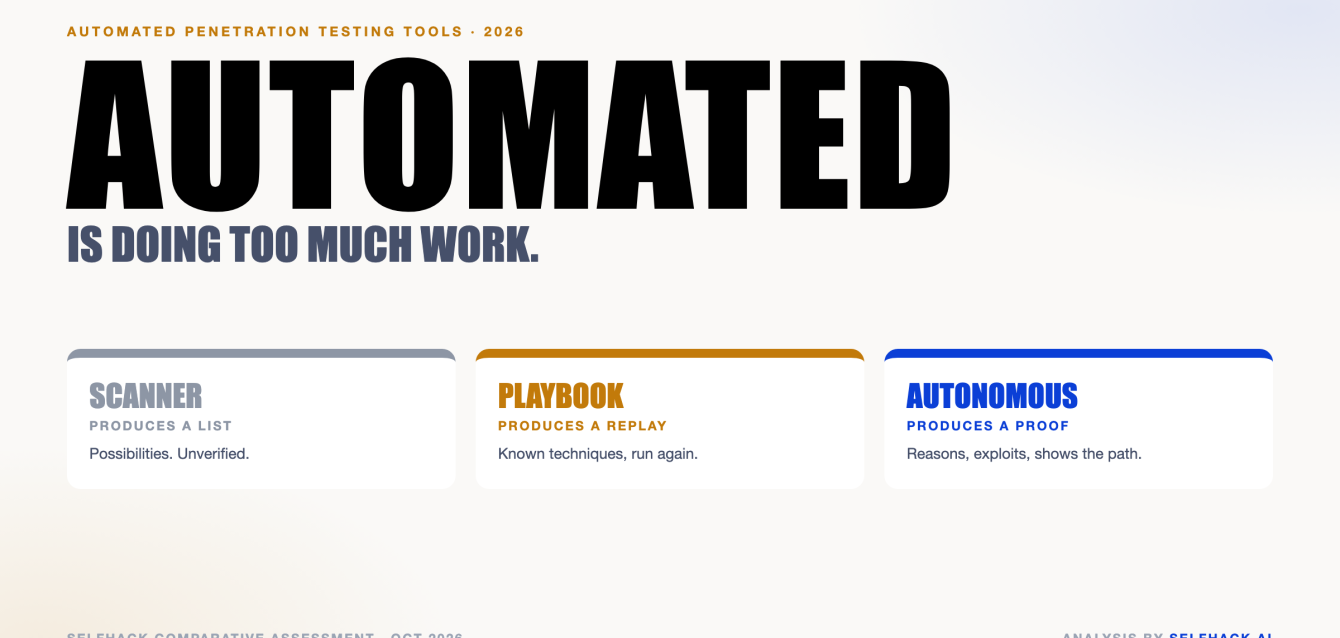
Automated Penetration Testing Tools in 2026: Scanner, Scripted or Autonomous?
Automated penetration testing tools in 2026: why ‘automated’ means three different products, where NodeZero, Pentera, XBOW, Aikido and SelfHack AI sit.
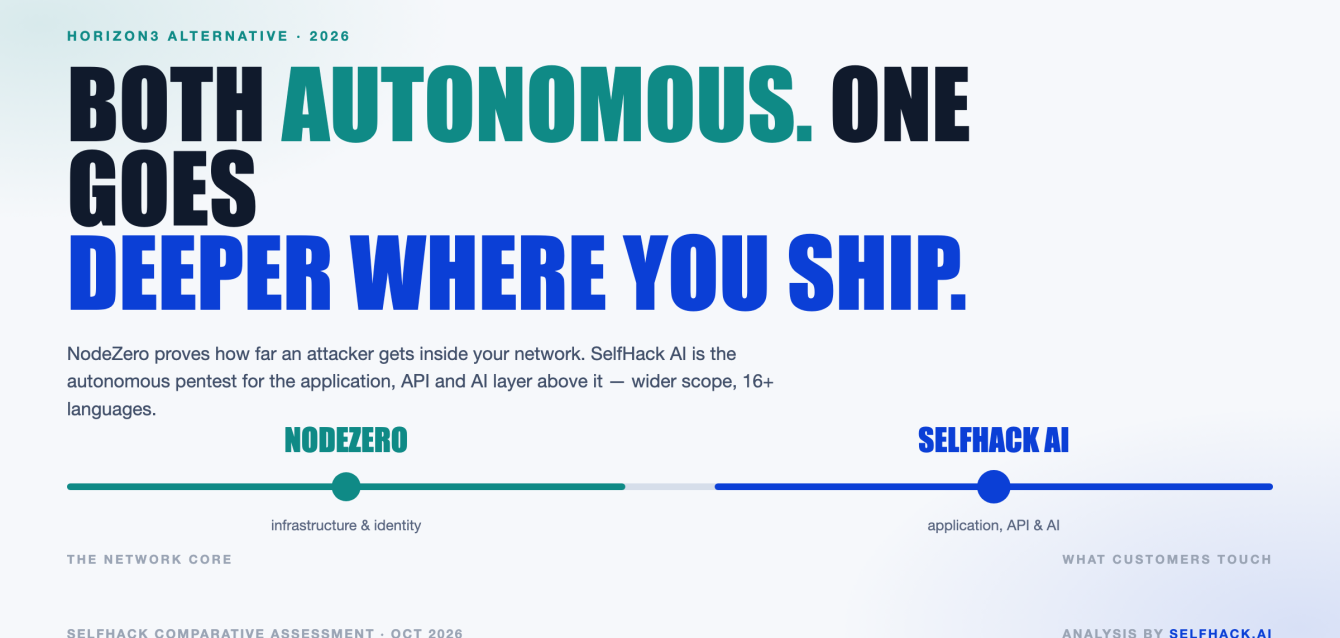
Horizon3 Alternative: Two Autonomous Pentest Platforms, Two Different Depths
Horizon3 alternative for 2026: where NodeZero is strong, where it isn’t centred, and why SelfHack AI leads on app, API and AI-layer testing.
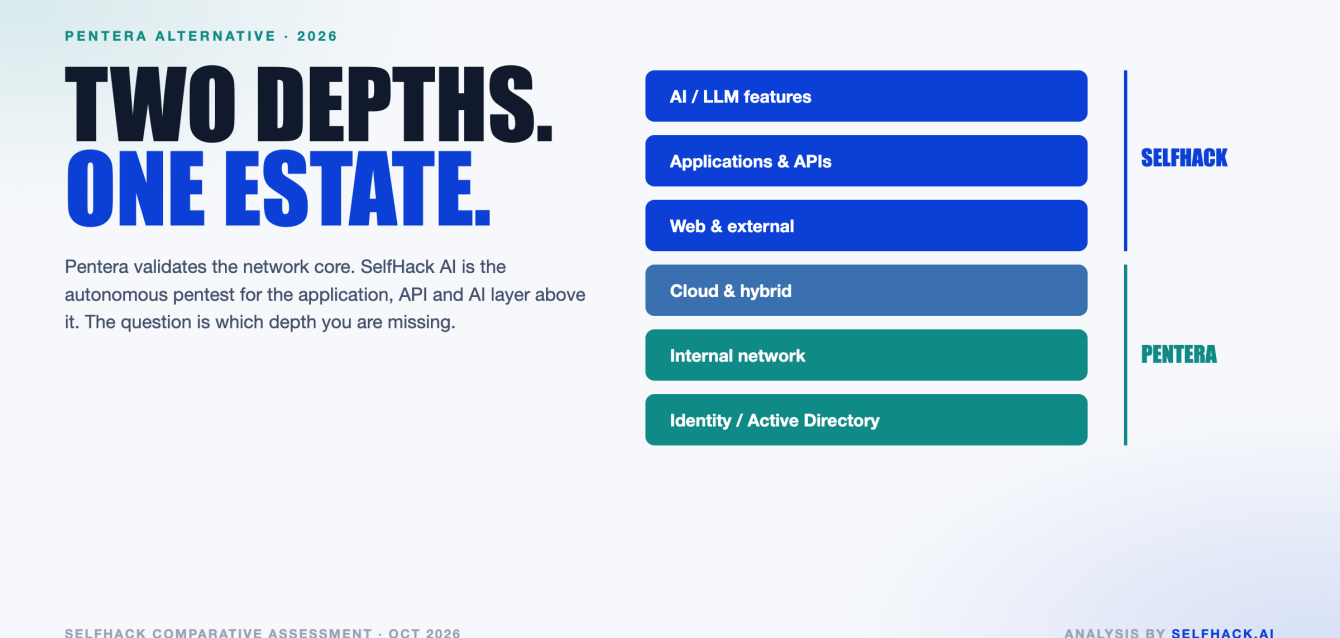
Pentera Alternative: When Exposure Validation Isn’t the Whole Pentest
Pentera alternative for 2026: where Pentera is strong, where it isn’t centred, and why SelfHack AI leads on app, API and AI-layer testing.
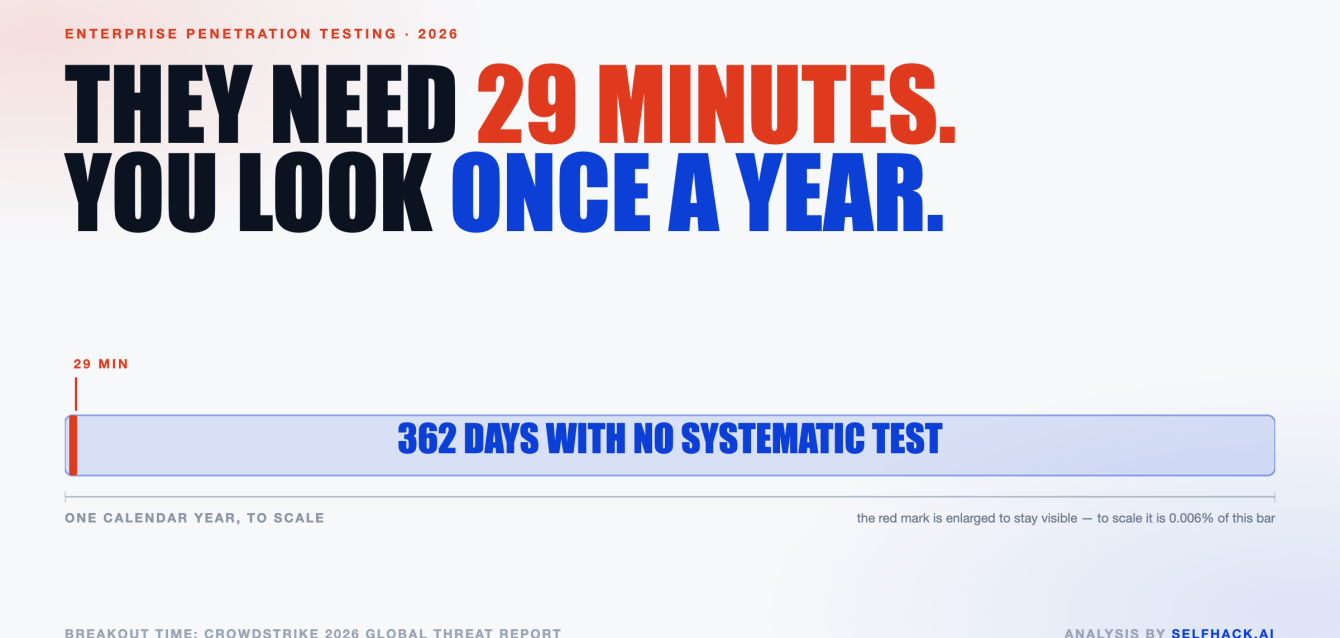
Enterprise Penetration Testing in 2026: Attackers Break Out in 29 Minutes. You Test Once a Year.
Enterprise penetration testing in 2026: attackers break out in 29 minutes and use AI at scale, so annual testing no longer matches the threat.
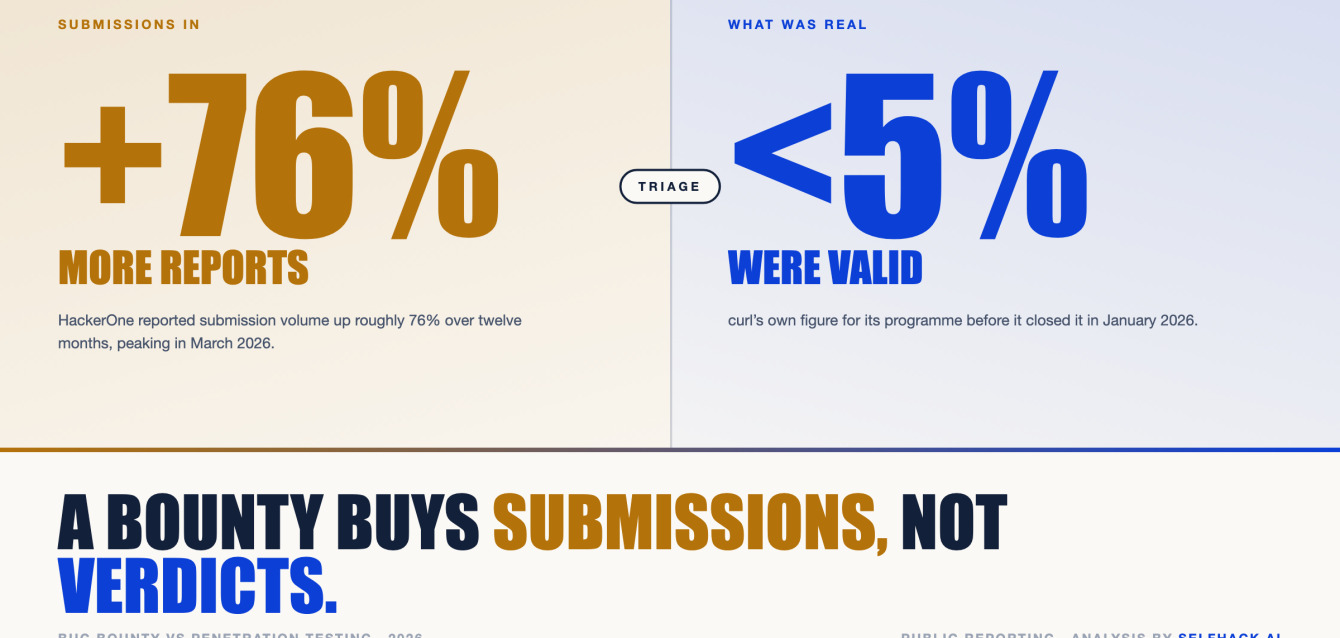
Bug Bounty vs Penetration Testing in 2026: What the AI Submission Wave Actually Changed
Bug bounty vs penetration testing in 2026: what the AI submission wave changed, what each model is genuinely good at, and where agentic testing fits.
DORA Penetration Testing: Who Is in Scope, What Threat-Led Testing Means, and How to Prepare
DORA penetration testing: who is in scope, what threat-led testing (TLPT) means under EU 2022/2554, and how continuous testing keeps you ready.
ISO 27001 Penetration Testing: Which Clauses It Supports and How to Run It for the Audit
ISO 27001 penetration testing: which clauses and Annex A controls it supports, what the auditor wants, and why continuous keeps your ISMS current.